When Technology Feels Fine but Exposure Is Already Growing
Most municipal leaders don’t think about technology until systems go down. That’s the moment it stops being a support function and becomes a crisis.
As long as email is working, employees can access files, backups are running somewhere in the background, and the outside IT provider appears to be handling tickets, there is a fairly natural assumption that things are probably in decent shape.
Most municipal administrators, supervisors, and department heads are not spending their week wondering who has elevated administrative rights inside Microsoft 365 or whether domain authentication was fully completed. Nor should that be where their attention has to live during normal operations.
But here’s what I’ve noticed: the technology issues creating the most exposure inside public offices are often not the loud, obvious failures that immediately pull everyone into crisis mode. They’re the quiet ones. The oversight areas that sit unnoticed because nothing feels urgent until leadership is asked a question they can’t answer with confidence.
Governance Questions That Sound Different Than They Used To
Some questions no longer stay inside the IT department.
Who approved employee use of AI tools? What information is being entered into those systems? Has anyone reviewed who has elevated access? Who owns the first hour of an incident response? Where are the municipality’s cyber controls documented?
These are governance concerns, and that distinction matters because the exposure no longer stays contained once something starts to unravel.
Payroll, resident communication, board packets, vendor payments, shared records, utility documentation, police and fire reporting, internal approvals, and finance workflows all move through connected systems now. That is why small technology problems can quickly turn into larger municipal disruptions. Microsoft 365 environments are larger and more collaborative than they were a few years ago. Insurance carriers are asking harder questions. Auditors are asking for clearer proof. Even email now carries fraud exposure many offices didn’t face a decade ago.
Technology is no longer simply helping the office function in the background. It’s tied directly to accountability, public trust, operational continuity, and legal defensibility.
Exposure Often Builds Through Four Quiet Patterns
Here’s where most public offices become more vulnerable than they realize. Exposure develops gradually in the areas that keep getting pushed into “important, but not pressing.”
Informal tools outpace governance. Employees start using AI tools because they’re trying to work faster — summarizing reports, cleaning up correspondence, or speeding up routine administrative work. But nobody stops to define what information should never enter those systems.
Access expands and never gets reviewed. Broad permissions make support easier. Nobody circles back to narrow them again. Microsoft 365 collaboration grows the way it always does: more shared folders, more Teams sites, more users with inherited visibility, more records living in places that once made sense.
Decision ownership stays unclear. Many municipalities assume that if something serious happens, the outside IT provider will step in and guide the technical side. What hasn’t been discussed is how much internal decision-making still needs to happen immediately, long before the situation feels under control. Someone has to determine who authorizes a shutdown. Someone has to contact cyber insurance. Someone has to control internal communication, preserve evidence, communicate with elected officials or department heads, and decide what should or should not be restored first. Those are decisions that should have been made before the incident, not during it.
Email trust becomes a vulnerability. Most public agencies don’t fully appreciate how much trust is attached to their email domain until someone exploits it. Residents trust messages that appear to come from familiar municipal addresses. Vendors trust payment requests that look like they originated from finance. Without proper domain authentication controls—DMARC, SPF, DKIM—that trust is easier to abuse than most offices realize. At that point, the problem isn’t just suspicious email. It becomes a communication integrity problem. A payment fraud problem. Sometimes a public confidence problem.
That’s the inflection point. Each individual area feels manageable enough to postpone one more month. By the time someone finally steps back and looks at the whole picture, what looked like a few minor unfinished areas has become a much broader pattern of unowned oversight.
The real problem isn’t the technical deficiency. It’s the ownership gap behind it.
What Better Oversight Looks Like
The local governments handling this best aren’t the ones with the most software layered into the environment. They’re the ones that stopped treating cybersecurity as something vaguely outsourced in the background and started treating it as a governed operational responsibility.
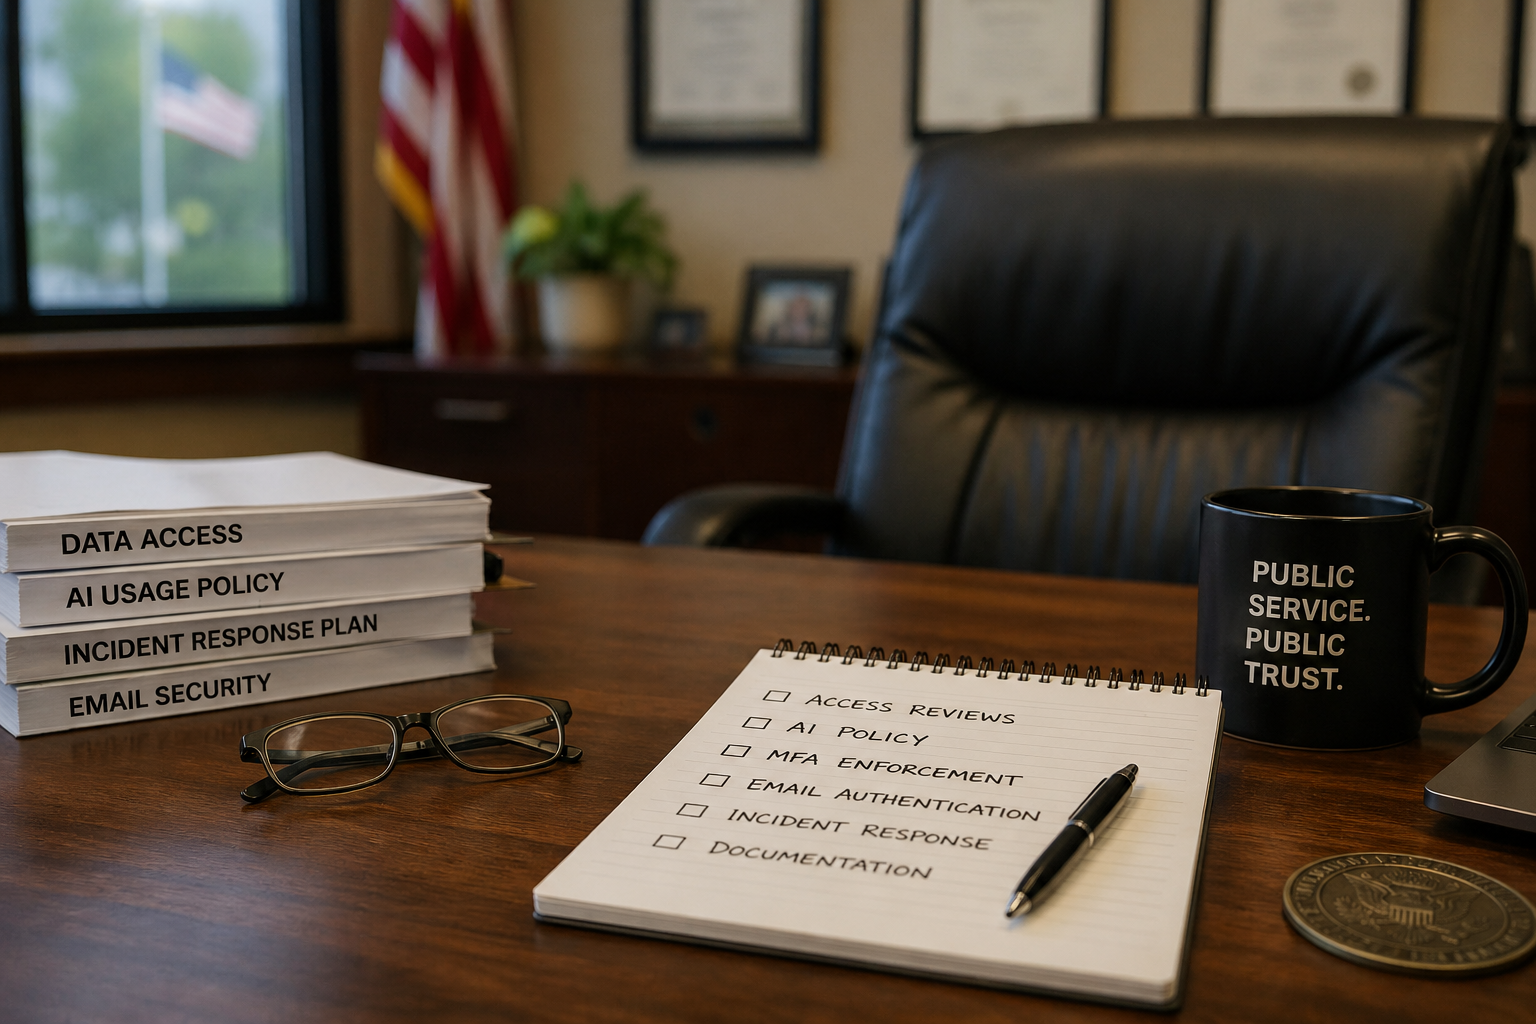
Leadership has visibility into what AI use is permitted. Teams review permissions intentionally. Microsoft 365 access gets revisited with discipline. Domain authentication is enforced. Incident response ownership is documented.
Cyber controls are tracked in one place. The municipality knows what has been addressed and what still needs work.
None of this requires leadership to become deeply technical. It requires leadership to stop assuming oversight exists simply because technology exists.
It also means documenting controls before oversights become claims. The assumption that something is covered and the ability to demonstrate it are rarely the same thing.
Why Technology Exposure Builds Until Leadership Has to Explain It
Many of the technology exposures affecting local governments today don’t arrive with alarms. They build quietly through informal AI use, accumulated permissions, undocumented response ownership, and unsecured email trust.
When leadership is eventually asked whether the municipality had reasonable oversight in place before an issue occurred, “we thought IT had it covered” is rarely the answer anyone wants to be giving.
The better answer is: we owned it.
Questions Leaders Are Asking
What technology oversights are creating the most liability exposure for local governments?
Exposure develops gradually in the areas that keep getting pushed into 'important, but not pressing.' The four patterns are: informal tools outpacing governance, access expanding and never getting reviewed, decision ownership staying unclear, and email trust becoming a vulnerability.
Why can't local governments rely on their outside IT provider to handle a cyber incident?
Many municipalities assume that if something serious happens, the outside IT provider will step in and guide the technical side. What hasn't been discussed is how much internal decision-making still needs to happen immediately, long before the situation feels under control. Someone has to determine who authorizes a shutdown, contact cyber insurance, control internal communication, preserve evidence, communicate with elected officials or department heads, and decide what should or should not be restored first.
How does unsecured email put a municipality at risk beyond just spam or phishing?
Without proper domain authentication controls—DMARC, SPF, DKIM—that trust is easier to abuse than most offices realize. At that point, the problem isn't just suspicious email. It becomes a communication integrity problem. A payment fraud problem. Sometimes a public confidence problem.
What does good cybersecurity oversight actually look like for a local government?
Leadership has visibility into what AI use is permitted. Teams review permissions intentionally. Microsoft 365 access gets revisited with discipline. Domain authentication is enforced. Incident response ownership is documented. Cyber controls are tracked in one place. The municipality knows what has been addressed and what still needs work.
Do municipal leaders need to become technical experts to manage cybersecurity risk?
None of this requires leadership to become deeply technical. It requires leadership to stop assuming oversight exists simply because technology exists. It also means documenting controls before oversights become claims. The assumption that something is covered and the ability to demonstrate it are rarely the same thing.