When Familiar Risks Become Invisible Risks
The biggest risks in most organizations aren’t the ones people don’t know about. They’re the ones people have stopped noticing, usually because they’ve become normal, not because they’re hidden.
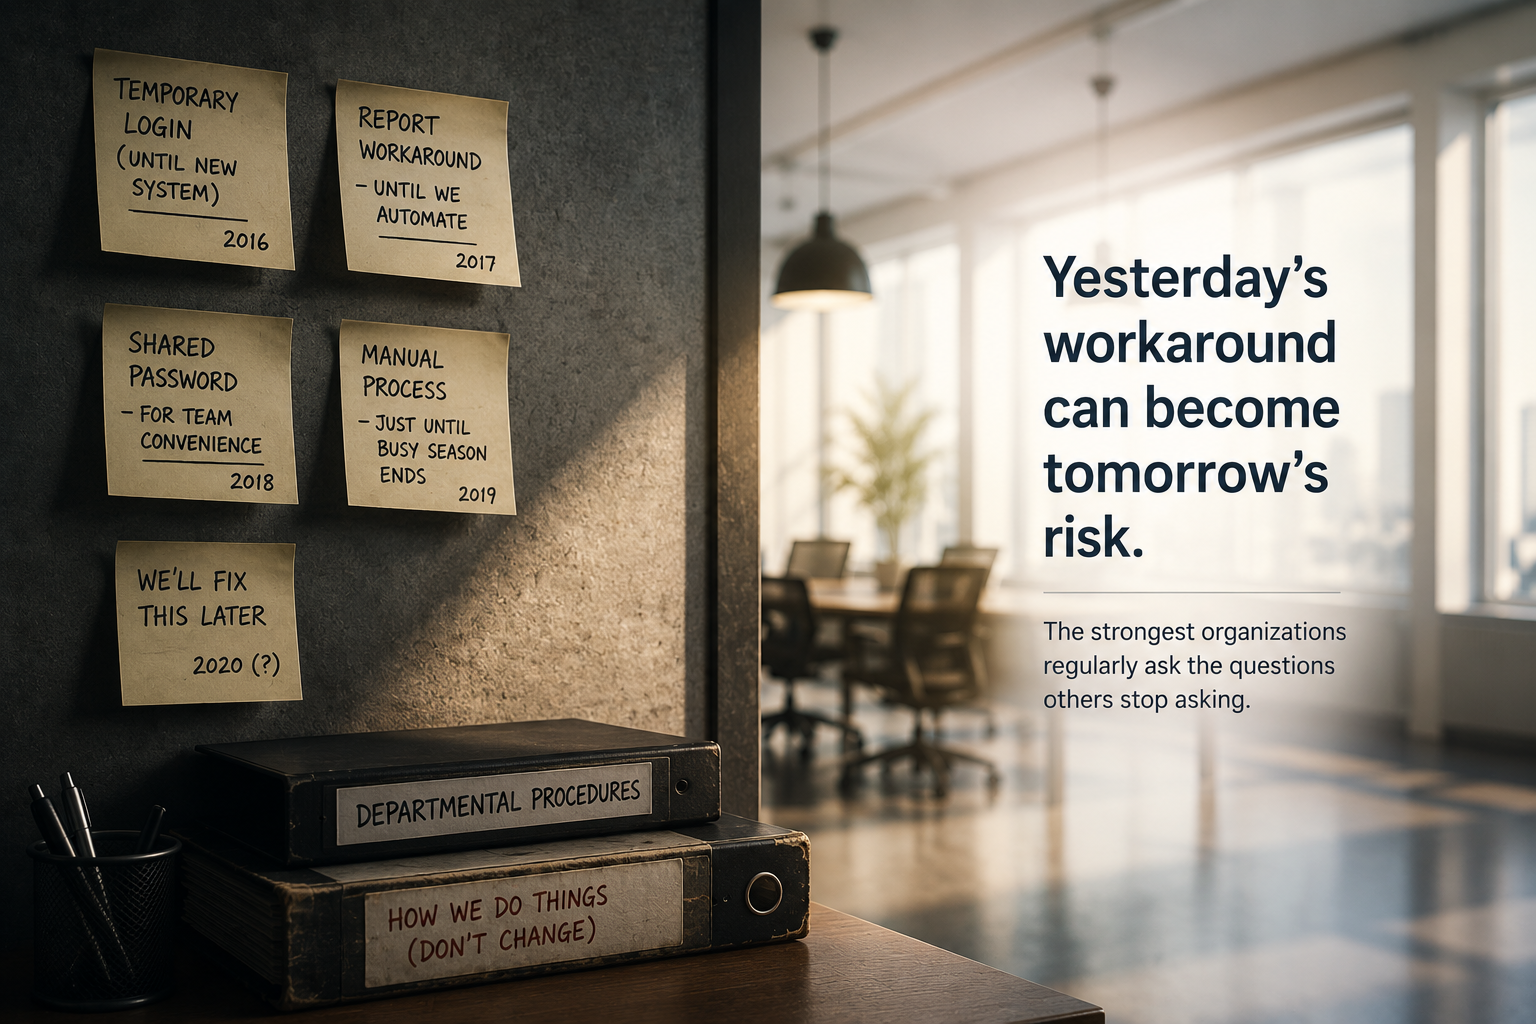
Every organization has examples. A report still generated the same way it was ten years ago. A shared account that everyone knows about but no one owns. A spreadsheet that somehow became part of a critical process. A sticky note that was supposed to be temporary but is now treated like official documentation. In a municipality, that might be a payroll process, a recurring state report, a vendor portal, or a department account that has been handled the same way for years.
Most of these didn’t start because someone was careless. In fact, they probably started as practical solutions to real problems. That’s what makes them so easy to accept, and so easy to stop questioning.
How Risk Becomes Normal
There’s usually a point when a risk stops looking like a risk and simply starts looking like the process. Maybe it’s the workaround that solved an urgent problem three years ago and never got formalized. Maybe it’s the manual step that everyone knows should be automated, but it works well enough right now. Maybe it’s the responsibility nobody officially owns, so it gets done inconsistently by whoever remembers.
At first, these situations feel temporary. We tell ourselves: “We’ll fix that next quarter.” Next quarter comes and nothing changes. Then the people who remember the original problem leave. New people inherit the workaround without the context. It stops looking like a gap and starts looking like how things are done.
That’s when a visible risk becomes an invisible one.
Eventually, nobody remembers why the workaround exists anymore. The person who created it left, someone else inherited it, and by the time a new leader arrives, there is no context left. There is only the assumption that it must have been necessary because it is still there.
Why Leaders Often Don’t See Organizational Risk
Here’s where it gets tricky: leadership doesn’t see it because leadership doesn’t encounter it the way operations does. If you run a police department, you don’t spend your day in the dispatch system or managing the evidence locker. If you run finance, you’re not the one manually reconciling those spreadsheets. So you don’t see the workaround. You see the output. The incident report got filed. The budget closed. The payroll went out. And if the output looks right, the invisible risk stays invisible.
There’s another layer too. By the time something has become normal, it’s also become defended. The person who knows how to work around it has become the person who knows how to get things done. They’re competent. They’re relied upon. If you question the workaround, you’re implicitly questioning their judgment. So people don’t. The risk becomes protected by relationships.
How Unquestioned Workarounds Create Cybersecurity Risk
This is one of the reasons I believe cybersecurity is often misunderstood in local government.
Many people think cyber risk begins when an attacker finds a vulnerability. More often, it begins much earlier. It begins when an old workaround quietly becomes part of normal operations.
A shared password isn’t simply an authentication issue. It’s evidence that a temporary decision was never revisited. A former employee’s access isn’t just an IT oversight. It’s a reminder that no one paused to ask whether yesterday’s permissions still matched today’s responsibilities. A report only one person knows how to generate isn’t a software problem. It’s organizational knowledge that never became organizational property.
The same pattern extends to vendor and cloud systems. If the platform works every day, few people stop to ask how dependent the organization has become on it.
That is why the strongest cybersecurity conversations have very little to do with security tools. They are questions about who owns something, who still has access, what has actually been tested, and whether anyone besides one employee knows how a process works. When those conversations are delayed, an incident can expose the gap very quickly. The difference between a measured response and a chaotic one often comes down to whether ownership, accountability, and documentation were clear before the pressure arrived.
The Leadership Question Every Organization Should Revisit
Every organization carries decisions that made perfect sense at one point in time. Most of them aren’t harmful. Some are still exactly the right approach. The challenge is knowing which ones quietly crossed the line from temporary solution to unquestioned routine.
That’s why I think one of the most valuable questions a leadership team can ask has nothing to do with cybersecurity. It’s this:
What have we stopped questioning simply because we’ve become used to it?
A Simple Familiar Risk Review for Municipal Leaders
A useful review does not need to start with a major audit. It can start with a short leadership conversation about the things that have become normal.
What are we assuming works because nothing has failed recently?
Backups, vendor support, email, Microsoft 365 access, payroll workflows, and department reporting may all look stable until someone asks how they were last tested or reviewed.
What process depends too heavily on one person?
If only one employee knows how to complete a report, contact a vendor, prepare a recurring file, or work around a system limitation, the process may be more fragile than it appears.
What access exists because it has always existed?
Shared accounts, old permissions, former employee access, vendor credentials, and administrative rights often survive because no one owns the final review.
What workaround has quietly become normal?
A spreadsheet, emailed attachment, saved desktop file, shared password, or informal approval path may have started as a practical fix. Over time, it becomes an unofficial process with no control around it.
What would be hard to prove if someone asked tomorrow?
If leadership cannot produce evidence of restore testing, access reviews, MFA enforcement, vendor oversight, or incident response planning, the risk may be more familiar than managed.
The Strongest Leaders Notice What Everyone Else Has Stopped Seeing
The point is not to question everything endlessly. The point is to identify where comfort has replaced verification. That is where familiar risk usually lives.
That question reaches far beyond technology. It touches operations, continuity, accountability, institutional knowledge, and ultimately resilience. For public-sector organizations, those stakes are concrete. Operational continuity and accountability become visible the moment systems fail, services slow, or residents start asking questions.
Because organizations rarely become more vulnerable overnight. More often, vulnerability arrives so gradually that it begins to feel normal.
The strongest leaders make time to notice what everyone else has stopped seeing.
Questions Leaders Are Asking
Why do organizations stop noticing their own risks over time?
The biggest risks in most organizations aren't the ones people don't know about. They're the ones people have stopped noticing, usually because they've become normal, not because they're hidden. Most of these didn't start because someone was careless. In fact, they probably started as practical solutions to real problems. That's what makes them so easy to accept, and so easy to stop questioning.
Why don't leaders see the operational risks happening inside their own organizations?
Leadership doesn't see it because leadership doesn't encounter it the way operations does. If you run a police department, you don't spend your day in the dispatch system or managing the evidence locker. So you don't see the workaround. You see the output. And if the output looks right, the invisible risk stays invisible. There's another layer too. By the time something has become normal, it's also become defended. The person who knows how to work around it has become the person who knows how to get things done. If you question the workaround, you're implicitly questioning their judgment. So people don't. The risk becomes protected by relationships.
How do unquestioned workarounds create cybersecurity risk?
Many people think cyber risk begins when an attacker finds a vulnerability. More often, it begins much earlier. It begins when an old workaround quietly becomes part of normal operations. A shared password isn't simply an authentication issue. It's evidence that a temporary decision was never revisited. A former employee's access isn't just an IT oversight. It's a reminder that no one paused to ask whether yesterday's permissions still matched today's responsibilities.
What questions should municipal leaders ask to identify familiar risks in their organization?
What are we assuming works because nothing has failed recently? What process depends too heavily on one person? What access exists because it has always existed? What workaround has quietly become normal? What would be hard to prove if someone asked tomorrow?
How does a temporary workaround eventually become an invisible organizational risk?
At first, these situations feel temporary. We tell ourselves: 'We'll fix that next quarter.' Next quarter comes and nothing changes. Then the people who remember the original problem leave. New people inherit the workaround without the context. It stops looking like a gap and starts looking like how things are done. Eventually, nobody remembers why the workaround exists anymore. There is only the assumption that it must have been necessary because it is still there.